
Organizations worldwide face mounting pressure to protect sensitive data while enabling employees to access the web freely. Traditional security tools struggle to keep pace with sophisticated phishing attacks, zero-day exploits, and malware delivered through seemingly legitimate websites. Authentic8 Silo addresses this challenge through a fundamentally different approach: moving web browsing entirely off the endpoint and into a secure, isolated cloud environment. This remote browser isolation technology creates a protective barrier between users and internet threats, ensuring that malicious code never reaches corporate networks or devices.
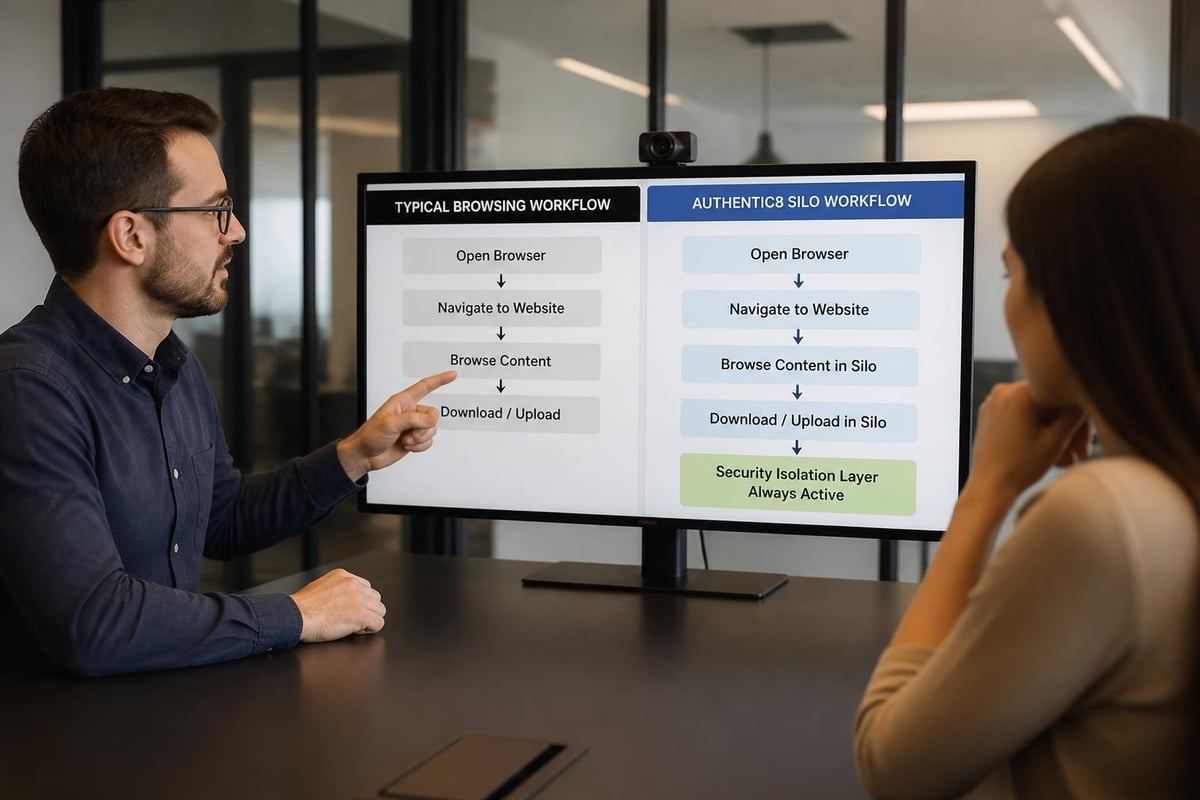
Authentic8 Silo operates on a deceptively simple principle: execute all web browsing activity in a remote, disposable environment rather than on the user's local machine. When someone accesses a website through Silo, the actual rendering, JavaScript execution, and content processing happen in a hardened cloud container managed by Authentic8. The user receives only a visual stream of the browsing session, similar to watching a video of someone else browsing the web.
This architectural separation delivers profound security benefits. Malicious downloads, drive-by exploits, and credential-harvesting scripts execute in the isolated container, not on the endpoint. Once the session ends, the container is destroyed, eliminating any persistence mechanisms that malware might attempt to establish.
The technical implementation involves several coordinated components working together seamlessly:
Each browsing session launches in a fresh container with no data carried over from previous sessions. This stateless approach ensures that even if malware compromises one session, it cannot affect subsequent browsing or other users.
Organizations can deploy Authentic8 Silo without installing thick clients or significantly modifying existing infrastructure. Users typically access Silo through a lightweight connector or directly via a web portal, depending on the deployment model chosen by IT administrators.
Authentic8 Silo delivers enterprise-grade security through multiple layers of protection that address both known and emerging threats. The platform's security posture reflects years of refinement in high-stakes government and enterprise environments.
Every web interaction occurs in a container that has no access to corporate resources, local files, or network shares. This isolation extends to:
The NIST guidelines on active content and mobile code emphasize isolation as a critical defense against web-based attacks, a principle central to Silo's design philosophy.
Authentic8 Silo maintains rigorous third-party certifications that validate its security controls and operational practices. The platform holds FedRAMP authorization, making it suitable for federal agencies and contractors handling government data. Additional certifications include SOC 2 Type II, HIPAA compliance, and ISO 27001, as detailed on the Authentic8 certifications page.
These certifications matter because they represent independent verification that Silo meets stringent security requirements across multiple frameworks. Organizations subject to regulatory oversight can leverage these existing certifications to accelerate their own compliance efforts.
| Certification | Relevance | Key Benefit |
|---|---|---|
| FedRAMP Moderate | Government agencies, contractors | Pre-authorized for federal use |
| SOC 2 Type II | Enterprise buyers, financial services | Operational controls validated |
| HIPAA | Healthcare providers, insurers | PHI protection mechanisms certified |
| ISO 27001 | International organizations | Global information security standard |
Authentic8 Silo supports flexible deployment options that accommodate diverse organizational requirements and risk profiles. IT teams can tailor the implementation to match their specific security policies and user needs.
The standard deployment runs entirely in Authentic8's cloud infrastructure, requiring minimal on-premises infrastructure. Organizations simply configure user access, define policies, and begin routing traffic through Silo. This model offers the fastest time-to-value and lowest operational overhead.
Cloud deployment works particularly well for:
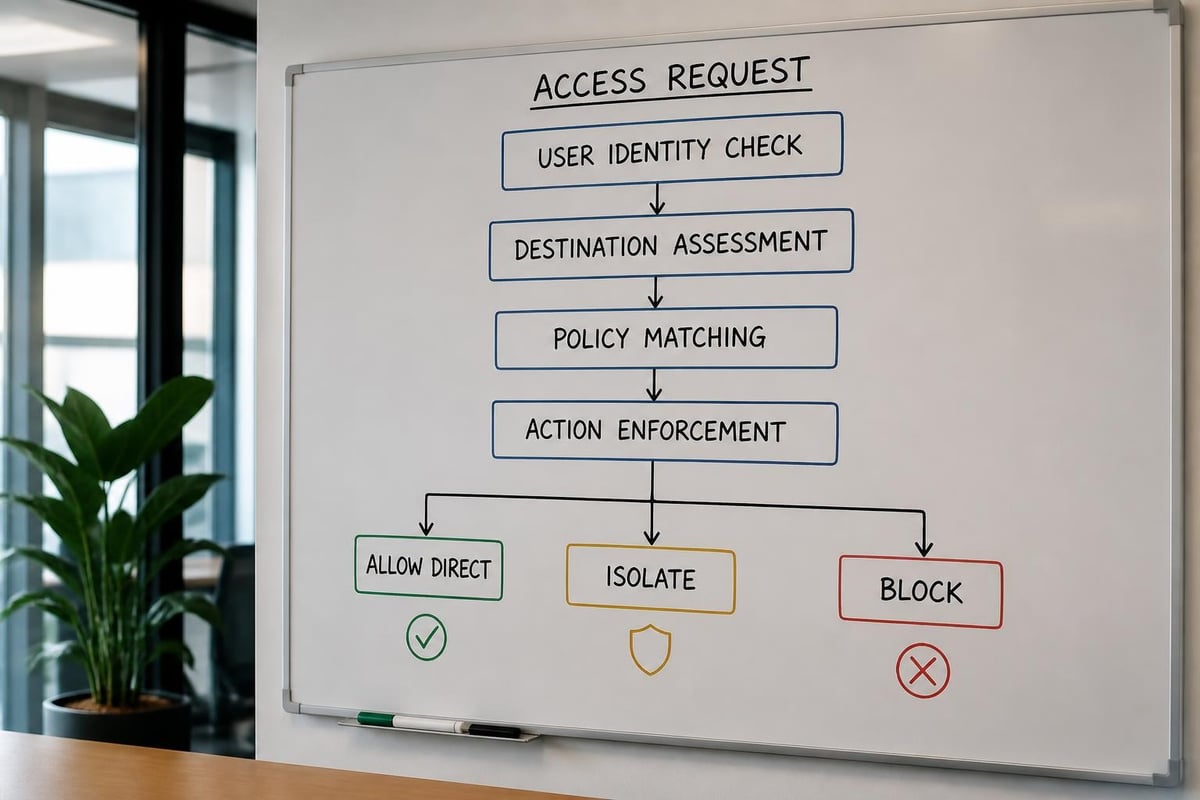
Administrators define granular policies that control how users interact with web content. These policies can restrict or permit specific actions based on website category, URL, user role, or data classification. Common policy configurations include:
The Silo Apps architecture enables administrators to create preconfigured workspaces with embedded tools and resources, streamlining access to frequently used web applications while maintaining security.
Modern enterprises deploy dozens of security tools, and adding another platform raises legitimate concerns about complexity and interoperability. Authentic8 Silo addresses these concerns through extensive integration capabilities that complement existing investments.
Silo integrates with major identity providers including Active Directory, Okta, Azure AD, and other SAML 2.0-compliant systems. This integration enables:
Users authenticate once and gain access to isolated browsing sessions without managing separate credentials or certificates.
Organizations generate security value from their tools only when those tools share information effectively. Silo exports detailed logs and telemetry to SIEM platforms, enabling security teams to:
The platform's logging captures URLs visited, files transferred, policy violations, and user actions, providing forensic visibility into web-based activities.
Security solutions fail if users circumvent them due to poor performance or usability friction. Authentic8 Silo balances robust protection with an experience that closely approximates native browsing.
The streaming protocol Silo employs adapts to available bandwidth, ensuring usable performance even over constrained connections. The platform maintains data centers in multiple geographic regions, allowing organizations to route traffic through nearby infrastructure and minimize latency.
Most users report browsing experiences that feel nearly identical to local browsing, with minimal perceptible delay. Graphics-intensive sites or streaming video may show slight compression artifacts, but text-based applications and standard web content render clearly.
Despite the isolation, Silo supports essential productivity functions:
These features ensure that security doesn't become an impediment to legitimate work activities.
Enterprise security solutions represent significant investments, and organizations rightfully scrutinize the total cost of ownership before committing. Authentic8 Silo pricing reflects its positioning as an enterprise-grade platform with substantial infrastructure requirements.
Authentic8 typically licenses Silo on a per-user, annual subscription basis. Pricing varies based on:
Organizations should budget for both licensing costs and any integration or professional services needed during initial deployment. The remote browser isolation market continues growing rapidly, with vendors offering various pricing approaches from per-user to per-session models.
Calculating ROI requires considering both direct costs avoided and indirect benefits realized:
| Cost Category | Impact |
|---|---|
| Incident response | Reduced malware infections decrease investigation and remediation costs |
| Data breach prevention | Avoiding even a single breach often justifies years of Silo licensing |
| Compliance fines | Meeting regulatory requirements prevents penalties and audit findings |
| Productivity loss | Fewer infections mean less user downtime and IT support burden |
Organizations with significant web-based threat exposure typically achieve positive ROI within the first year of deployment, particularly when accounting for the cost of incidents prevented.
Understanding how peers deploy authentic8 silo provides valuable context for organizations evaluating the platform. Public sector and commercial enterprises have documented successful implementations across various scenarios.
Federal agencies face unique security challenges, including sophisticated nation-state threats and strict compliance requirements. The U.S. Senate Commerce committee documentation references Authentic8 Silo procurement for law enforcement programs, highlighting its suitability for sensitive investigations.
Law enforcement investigators often need to access potentially malicious websites during cybercrime investigations without exposing agency infrastructure to compromise. Silo enables this research safely, while policy controls prevent accidental data leakage or unauthorized activities.
Regulated industries face dual pressures: protecting sensitive customer data while enabling employees to perform research and access external resources. Banks use Silo to allow employees to visit customer-reported phishing sites for investigation without risk of credential theft. Healthcare organizations protect patient information while permitting research into medical conditions and treatment options.
Just as organizations layer physical security measures to protect valuable assets (similar to how Limax Security Specialists provides comprehensive protection through multiple security product lines), digital security requires defense-in-depth approaches where browser isolation complements other controls.
No security technology delivers perfect protection without tradeoffs. Organizations evaluating authentic8 silo should understand its limitations and ensure alignment with their requirements.
Silo isolates web browsing but doesn't address:
Organizations need complementary controls for these scenarios rather than expecting Silo to solve all endpoint security challenges.
The ephemeral nature of isolated sessions creates challenges for workflows requiring persistent state. Users who rely on browser history, saved passwords (outside of password managers), or long-running sessions may need to adjust their habits.
Recent academic research, including studies on cookie isolation and browser partitioning, explores the security and usability tradeoffs inherent in strong isolation approaches. These studies validate the security benefits while acknowledging the user experience implications.
Applications requiring low latency or high bandwidth may not perform optimally through browser isolation. Examples include:
Organizations should test critical applications in Silo before committing to organization-wide deployment, and consider selective isolation policies that route only untrusted traffic through the platform.
Effective security programs integrate multiple technologies into cohesive architectures rather than deploying point solutions in isolation. Authentic8 silo fits into broader security frameworks as a specialized control for web-based threats.
Zero trust frameworks assume breach and verify every access request regardless of source. Silo advances zero trust principles by:
Organizations pursuing zero trust architectures often identify browser isolation as a key capability gap that traditional tools don't address adequately.
Silo works alongside other security controls to create defense-in-depth:
Each technology addresses different attack vectors and failure modes, creating overlapping layers of protection that increase overall resilience.
Organizations evaluating authentic8 silo should assess the platform against consistent criteria that reflect their specific requirements and risk tolerance.
Key technical factors include:
Request proof-of-concept deployments with your actual users and applications rather than relying solely on demonstrations with generic scenarios.
Beyond technology, evaluate:
Organizations with limited IT resources should prioritize vendors offering comprehensive professional services and managed options.
Review contract terms carefully, particularly:
Work with procurement and legal teams early in the evaluation process to identify and address potential concerns before vendor selection.
Browser isolation technology represents a fundamental shift in how organizations protect themselves from web-based threats, moving prevention from the endpoint to the cloud. Authentic8 Silo exemplifies this approach with enterprise-grade isolation, comprehensive policy controls, and proven deployment success across demanding environments. Just as Limax Security Specialists layers physical security measures to protect South African homes and businesses from intrusion, digital security requires thoughtful integration of complementary technologies that address evolving threats. Contact Limax Security Specialists to discuss how comprehensive security solutions can protect your organization's most valuable assets.


