
The landscape of network security and connectivity has transformed dramatically, with businesses demanding solutions that integrate advanced threat protection, intelligent routing, and centralized management. The cisco meraki mx family of security and SD-WAN appliances has emerged as a leading choice for organizations seeking to unify their network infrastructure while maintaining robust security postures. These cloud-managed devices combine unified threat management (UTM), next-generation firewall capabilities, and software-defined wide-area networking into a single platform, eliminating the complexity traditionally associated with deploying and maintaining enterprise-grade security infrastructure.
The cisco meraki mx platform represents a fundamental shift from legacy security appliances toward cloud-first network management. Each MX appliance connects to Meraki's cloud infrastructure, enabling administrators to configure, monitor, and troubleshoot from anywhere with internet access.
Every cisco meraki mx device leverages the Meraki Dashboard, a centralized web interface that eliminates the need for command-line configuration or on-premises management servers. This architecture provides several distinct advantages:
The cloud management model significantly reduces the technical expertise required for deployment. Security specialists can configure complex firewall rules, VPN tunnels, and content filtering policies through an intuitive interface rather than memorizing syntax. According to Meraki’s official installation guide, most deployments complete initial setup within 30 minutes.
The cisco meraki mx lineup spans from small-branch appliances to high-throughput data center models. Understanding the hardware differences ensures proper sizing for specific deployment scenarios.
| Model Series | Typical Use Case | Throughput | User Count | Key Features |
|---|---|---|---|---|
| MX64/65 | Small branch offices | Up to 250 Mbps | 25-50 users | Compact, cost-effective, built-in wireless |
| MX67/68 | Medium branches | Up to 450 Mbps | 50-200 users | Enhanced performance, PoE+ option |
| MX75 | Large branches | Up to 500 Mbps | 100-500 users | High availability ready, advanced routing |
| MX85 | Regional hubs | Up to 500 Mbps | 200-750 users | Dual WAN ports, higher session capacity |
| MX95 | Campus/datacenter | Up to 750 Mbps | 500-1000 users | Maximum throughput, enterprise features |
Performance specifications account for realistic workloads including firewall inspection, content filtering, and VPN encryption. An independent Miercom performance evaluation validated that cisco meraki mx appliances maintain consistent throughput even under heavy security processing loads.
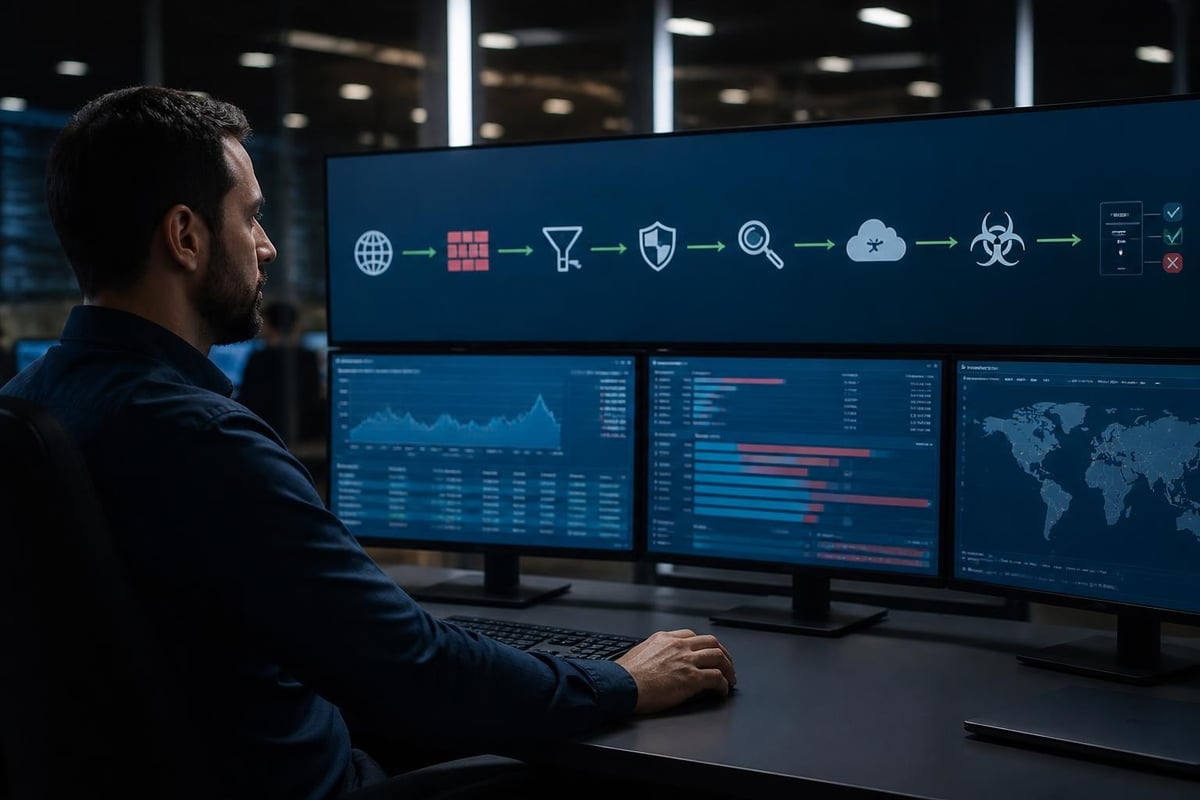
Modern security threats demand layered defense mechanisms that adapt to emerging attack vectors. The cisco meraki mx integrates multiple security functions into a cohesive protection framework.
Beyond traditional stateful packet inspection, MX appliances provide application-aware filtering and advanced threat detection:
The firewall operates on a policy-based model where administrators define rules based on source/destination networks, applications, or user groups. Processing occurs in a specific order-understanding this hierarchy prevents configuration conflicts that could inadvertently block legitimate traffic. Meraki’s firewall documentation details the exact processing sequence for layer 3 and layer 7 rules.
Organizations require granular control over internet usage without creating overly restrictive environments that hinder productivity. The cisco meraki mx provides several content filtering approaches:
Category-based blocking covers 60+ predefined categories including malware distribution sites, phishing domains, adult content, and social media platforms. Administrators select which categories to block or warn users before allowing access.
Custom URL lists supplement category filtering with organization-specific allow/deny lists. This proves particularly valuable for blocking newly registered domains that haven't been categorized or permitting legitimate sites incorrectly flagged.
Safe search enforcement automatically applies restricted search settings to major search engines, preventing users from disabling built-in filters.
Content filtering operates at the DNS and HTTP/HTTPS levels, intercepting requests before they reach destination servers. For encrypted traffic, MX appliances can perform TLS decryption and inspection, though this requires certificate deployment and introduces privacy considerations.
Software-defined WAN capabilities represent one of the cisco meraki mx platform's most compelling features, transforming how organizations connect distributed locations.
Traditional VPN configuration demands extensive planning, manual endpoint setup, and ongoing maintenance as networks evolve. Meraki's Auto VPN feature revolutionizes this process:
When a new cisco meraki mx is deployed and assigned to an existing network, it immediately discovers all peer devices and establishes encrypted tunnels without administrator intervention. This dramatically reduces deployment time for multi-site organizations.
Not all network traffic requires the same treatment. The cisco meraki mx analyzes application characteristics and network conditions to make real-time routing decisions:
A financial services firm might configure their cisco meraki mx to always route point-of-sale traffic over the primary fiber connection while sending general web browsing over a secondary cable link. If the fiber connection experiences latency spikes, the MX automatically shifts POS traffic to the backup link.
Successful cisco meraki mx implementations require thoughtful planning around network topology, security policies, and operational procedures.
The cisco meraki mx supports three primary deployment modes, each suited to different infrastructure scenarios:
Routed Mode positions the MX as the network gateway, performing NAT and serving as the default route for all clients. This represents the most common deployment, providing complete visibility and control over traffic.
One-armed concentrator connects the MX to an existing network without replacing the current gateway. VPN traffic and specific subnets route through the MX while other traffic follows existing paths. This mode suits organizations with established routing infrastructure.
Passthrough/bridge mode places the MX inline without NAT, preserving existing IP addressing schemes. Security features remain active while routing functions are delegated to other devices.
According to Meraki’s best practice design guide, routed mode delivers optimal performance and simplest troubleshooting for most deployments.
Mission-critical environments demand redundancy that prevents single points of failure. The cisco meraki mx supports warm spare high availability, pairing two identical appliances at a single location:
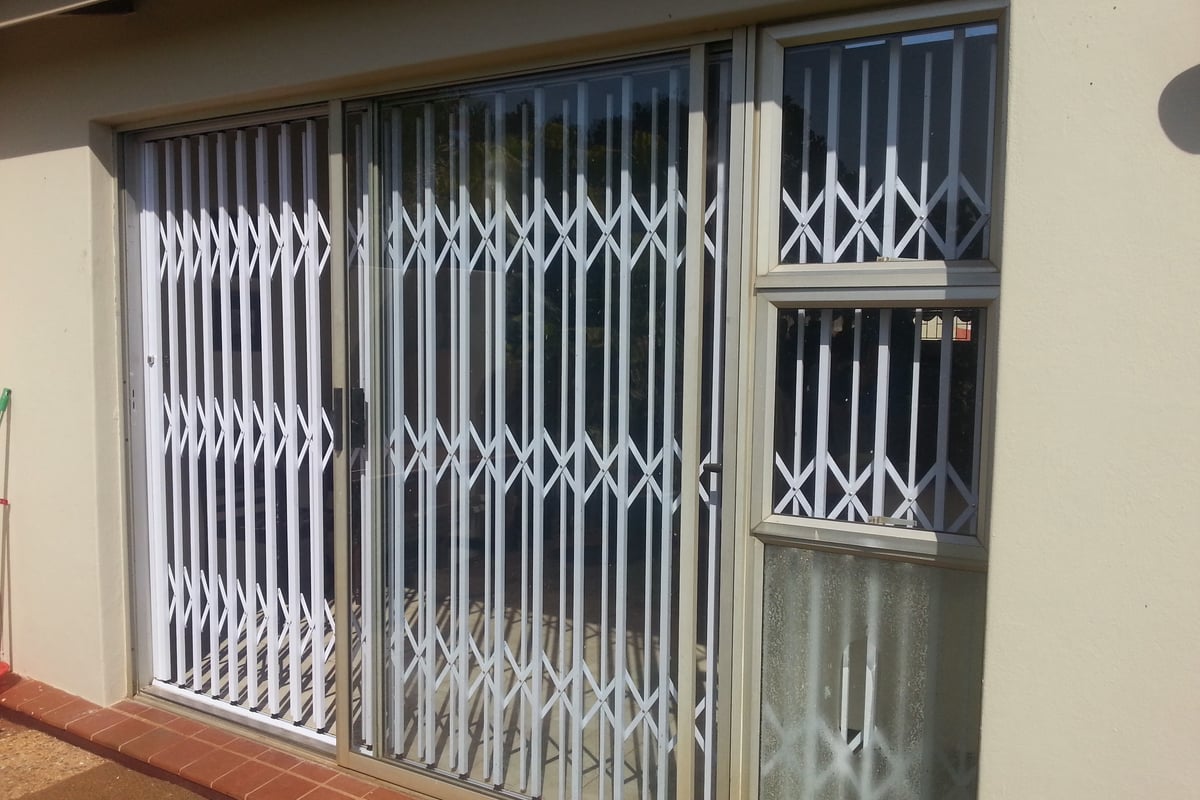
Physical security installations often mirror network security requirements. Just as network infrastructure demands redundancy and fail-safe mechanisms, physical access control systems require reliable protection that doesn't create vulnerabilities. Organizations seeking to secure premises alongside networks should consider integrated approaches-for example, deploying monkey-proof security gates that prevent unauthorized access while maintaining aesthetic appeal, complementing the network-layer security provided by cisco meraki mx appliances.
Effective security policies balance protection against usability. Overly restrictive rules frustrate users and encourage workarounds, while permissive policies expose organizations to threats.
Start with visibility before enforcement. Deploy the cisco meraki mx in monitoring mode initially, analyzing traffic patterns for several weeks to understand application usage and bandwidth consumption. This baseline prevents accidentally blocking business-critical applications.
Implement graduated enforcement. Rather than immediately blocking categories, configure warning pages that inform users they're accessing potentially problematic content. Repeated violations can then trigger actual blocks.
Document exceptions and review regularly. Every allow-list entry and bypass rule should include justification and an expiration date. Quarterly reviews ensure temporary exceptions don't become permanent security gaps.
| Policy Element | Recommended Approach | Common Pitfall |
|---|---|---|
| Outbound firewall | Default deny with explicit allows | Leaving default allow unchanged |
| Content filtering | Category-based with custom overrides | Blocking too broadly initially |
| IDS/IPS | Enabled in detection mode first | Enabling prevention without testing |
| VPN access | Group-based permissions | Individual user exceptions |
Beyond core security and SD-WAN functions, the cisco meraki mx ecosystem provides extended capabilities through integrations and advanced features.
The cisco meraki mx participates in Meraki's global threat intelligence network, receiving real-time updates about emerging threats and malicious IP addresses. Security events generate detailed logs showing:
Event data integrates with SIEM platforms via syslog forwarding, enabling correlation with broader security infrastructure. The TechTarget overview of Cisco Meraki MX capabilities highlights how this integration supports compliance reporting and incident response workflows.
Organizations with mobile workforces require secure remote access solutions. The cisco meraki mx includes built-in client VPN supporting:
Client VPN configuration requires certificate deployment and user authentication setup, but the Dashboard interface simplifies what traditionally demanded extensive command-line expertise.
Maintaining optimal cisco meraki mx performance requires ongoing monitoring and periodic tuning based on network evolution.
Unconstrained bandwidth consumption by non-critical applications degrades performance for business-essential traffic. The cisco meraki mx provides granular traffic shaping controls:
A common configuration dedicates 80% of available bandwidth to business applications while limiting recreational browsing and streaming to the remaining 20%. During peak hours, voice and video conferencing receive priority treatment regardless of overall utilization.
The Meraki Dashboard includes comprehensive troubleshooting capabilities that accelerate problem resolution:
Live packet capture initiated directly from the Dashboard without physical device access. Administrators specify capture filters and download PCAP files for analysis in Wireshark or similar tools.
Uplink monitoring continuously tests connectivity to internet endpoints, providing historical graphs of latency, packet loss, and uplink status. This visibility helps differentiate between MX issues and ISP problems.
VPN health checks display tunnel status, encryption details, and traffic statistics for each site-to-site connection, simplifying VPN troubleshooting.
Event log search filters security events, configuration changes, and system alerts by date range, event type, or specific devices.
The cisco meraki mx operates on a subscription licensing model that includes hardware support, cloud management, and security updates. Understanding licensing tiers ensures proper budgeting and feature access.
Three primary license levels provide increasing functionality:
Enterprise includes basic firewall, VPN, and SD-WAN features with application visibility. This entry-level license suits organizations requiring fundamental security without advanced threat protection.
Advanced Security adds intrusion prevention, advanced malware protection, and enhanced content filtering. Most deployments benefit from this tier's comprehensive threat defense.
Secure SD-WAN Plus bundles all security features with premium SD-WAN capabilities including performance-based routing and expanded application traffic shaping.
License terms range from one to ten years, with longer commitments offering per-year cost reductions. All licenses include 24/7 support, lifetime hardware warranty, and automatic updates-there are no hidden maintenance fees.
While cisco meraki mx licensing represents an ongoing operational expense, total cost of ownership (TCO) comparisons should account for:
Organizations accustomed to perpetual license models may initially hesitate at subscription pricing, but the operational efficiencies and included support typically offset license costs within the first year.
Technology investments must accommodate evolving business requirements and emerging threats. The cisco meraki mx platform's cloud-native architecture provides inherent adaptability.
Secure Access Service Edge (SASE) represents the convergence of network and security functions into cloud-delivered services. The cisco meraki mx aligns with SASE principles through:
Zero Trust networking assumes breach and verifies every access request regardless of source location. Cisco continues enhancing MX capabilities to support Zero Trust frameworks, with recent additions including microsegmentation and user-based firewall rules.
The Meraki Dashboard API enables programmatic configuration and monitoring, supporting infrastructure-as-code practices. Organizations can:
Automate bulk operations across hundreds of appliances using scripts rather than manual configuration.
Integrate with orchestration platforms like Ansible or Terraform for version-controlled network infrastructure.
Build custom dashboards pulling real-time metrics into business intelligence tools.
Trigger automated responses to security events through webhook integrations.
API access empowers security teams to extend cisco meraki mx functionality beyond native Dashboard features, creating tailored workflows matching specific operational requirements.
The cisco meraki mx platform delivers enterprise-grade security, intelligent routing, and simplified management that scales from single-location deployments to global networks. By consolidating multiple network functions into cloud-managed appliances, organizations reduce complexity while enhancing protection against evolving threats. Just as robust network security forms the foundation of digital infrastructure, physical security creates the first line of defense for facilities and assets. Limax Security Specialists brings the same commitment to comprehensive protection in the physical domain, offering expertly engineered security gates, burglar bars, and access control solutions that safeguard South African homes and businesses with reliability and style.


