
Organizations today face an evolving threat landscape where traditional security tools struggle to keep pace with sophisticated attacks. Enterprise security Splunk has emerged as a cornerstone platform for security operations centers worldwide, providing the visibility, correlation, and automation capabilities needed to detect, investigate, and respond to threats at scale. This comprehensive guide explores how security teams leverage Splunk Enterprise Security to protect critical infrastructure, streamline investigations, and maintain compliance across complex hybrid environments.
Splunk Enterprise Security (ES) is a premium security information and event management (SIEM) application built on top of the core Splunk platform. Unlike standalone security tools, enterprise security Splunk aggregates data from across your entire technology stack-network devices, endpoints, cloud services, identity systems, and applications-into a unified analytics environment.
The platform consists of several key architectural components that work together to deliver comprehensive security monitoring. At the foundation sits the Splunk indexer cluster, which ingests and stores massive volumes of machine data in real time. Search heads run the correlation searches, risk scoring, and threat intelligence lookups that power detection logic. Heavy forwarders collect data from remote sites and perform parsing before forwarding to indexers.
Enterprise deployments typically follow distributed architectures outlined in Splunk’s validated reference architectures, which provide tested configurations for various data volumes and use cases. Small to medium enterprises might deploy a single-site configuration with clustered indexers and search head clustering for high availability.
Large multinational organizations often implement multi-site indexer clusters with disaster recovery capabilities across geographic regions. These topologies ensure business continuity even during site failures while maintaining sub-second search performance across petabytes of security telemetry.
Capacity planning considerations include:
Resource allocation follows the "3:1 rule" where indexing capacity should support three times the average daily ingestion to handle burst scenarios. Search head specifications depend heavily on correlation search complexity and the number of concurrent dashboards.
Security operations teams deploy enterprise security Splunk across a wide spectrum of detection, investigation, and response workflows. The platform's flexibility allows organizations to address both traditional and emerging security challenges within a single pane of glass.
The heart of enterprise security Splunk lies in its correlation search engine, which continuously analyzes incoming data against detection rules mapped to the MITRE ATT&CK framework. These searches identify patterns indicative of malicious activity-from initial access attempts through lateral movement and data exfiltration.
Notable detections include detection of credential stuffing attacks by correlating failed authentication events across multiple services, identification of ransomware behavior through rapid file encryption patterns, and discovery of command-and-control communications by analyzing network flow anomalies. Risk-based alerting assigns scores to assets and identities, allowing analysts to prioritize investigations based on cumulative suspicious activity rather than isolated events.
| Detection Category | Data Sources | Typical Correlation Logic |
|---|---|---|
| Insider Threat | HR systems, DLP, file access | Unusual access + resignation indicators |
| Lateral Movement | Active Directory, endpoint logs | Privileged account usage across multiple systems |
| Data Exfiltration | Proxy, firewall, DLP | Large outbound transfers to rare destinations |
| Malware Execution | EDR, DNS, process creation | Known IOCs + suspicious parent-child relationships |
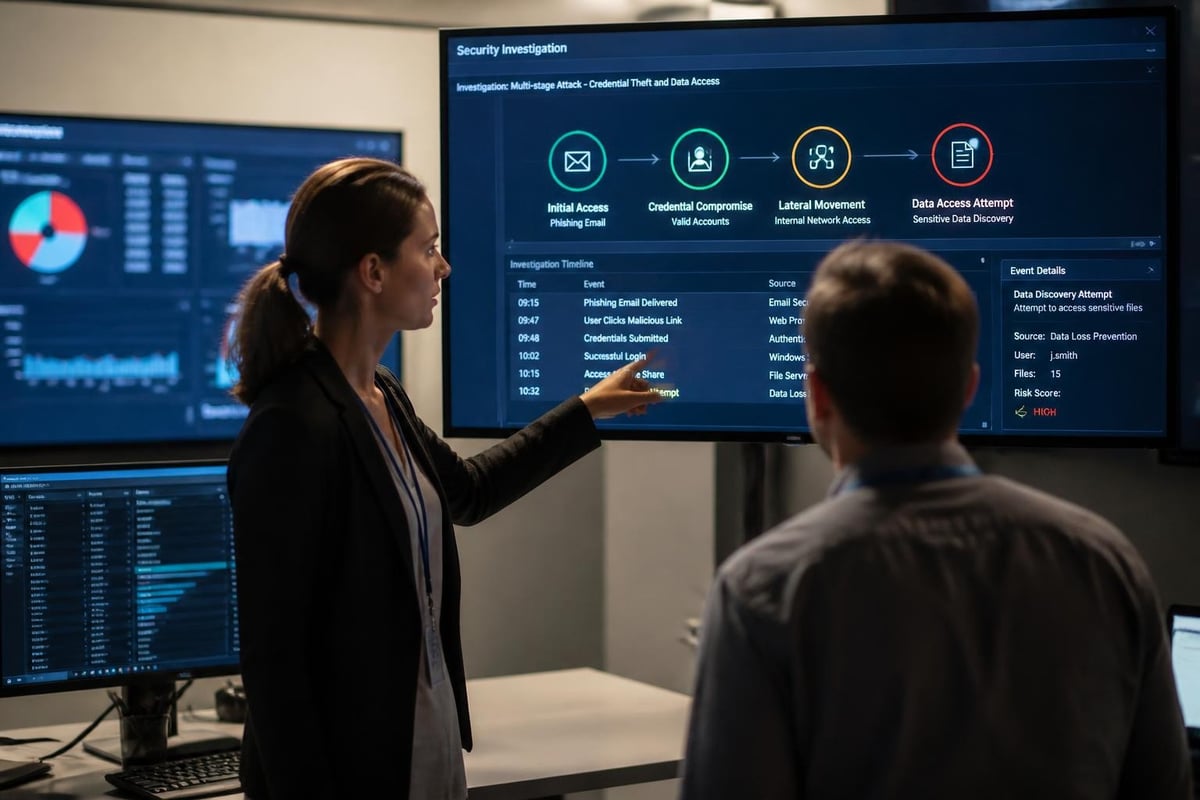
When enterprise security Splunk detects a threat, it can automatically trigger response workflows through integration with security orchestration platforms. Incident response teams use ES workspaces to document investigation timelines, attach relevant artifacts, and collaborate across distributed teams.
The platform maintains full audit trails of all investigation activities, supporting forensic reconstruction months or years after an incident. Automated enrichment pulls context from threat intelligence feeds, asset databases, and identity repositories to accelerate triage decisions.
Investigation acceleration features include:
Effective enterprise security Splunk deployments depend on comprehensive, high-quality data collection. Organizations must balance visibility requirements against ingestion costs and storage constraints, implementing strategic data source prioritization.
Following guidance from NIST SP 800-92 on log management, security programs should prioritize collection of authentication events, network traffic metadata, endpoint telemetry, and application transactions. These fundamental data types provide coverage across the majority of attack vectors observed in modern breaches.
Network visibility extends beyond traditional firewall logs to include DNS queries, proxy requests, NetFlow records, and SSL/TLS metadata. Endpoint data collection encompasses process creation, file modifications, registry changes, PowerShell executions, and service installations. Cloud environments require API-level monitoring of identity and access management changes, storage bucket modifications, and compute instance lifecycle events.
Physical security integrations deserve attention in comprehensive programs. Access control systems, video management platforms, and intrusion detection panels generate telemetry that correlates with cyber events. For example, an after-hours badge swipe followed by unusual database queries might indicate compromised credentials or insider activity.
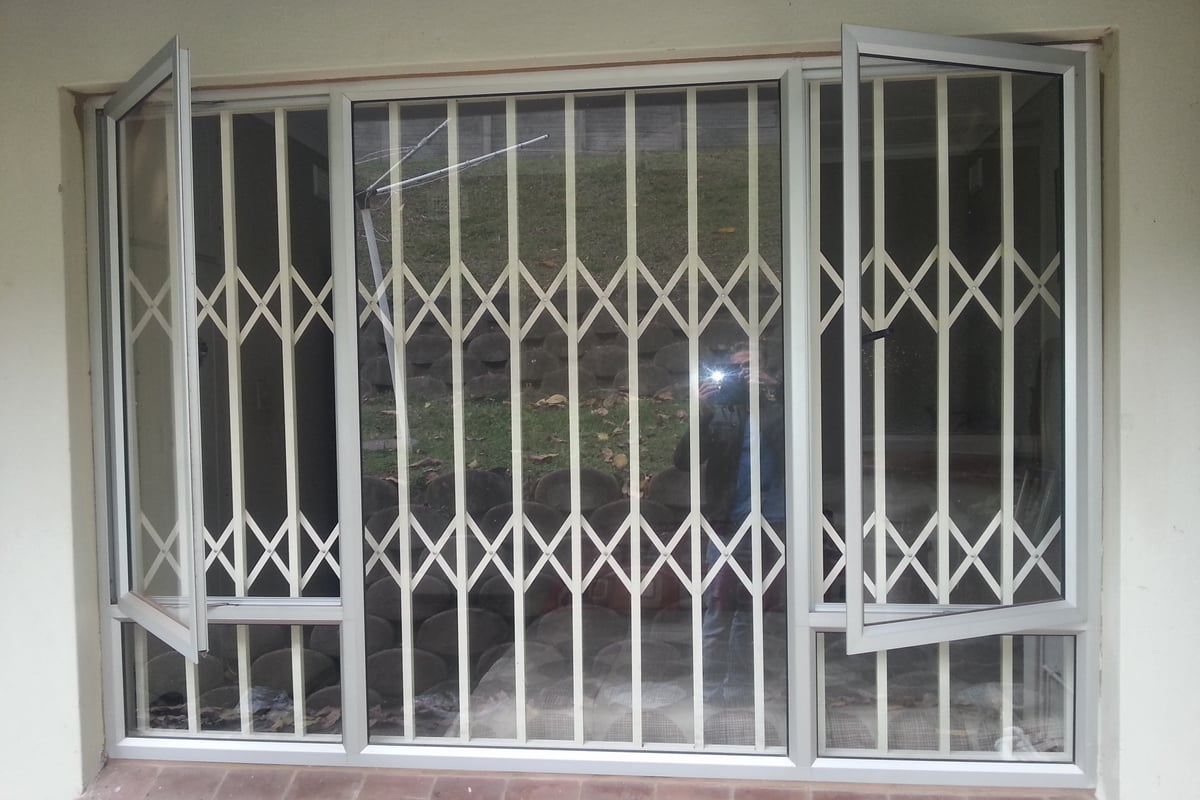
Physical security specialists working with organizations on protective measures understand the value of correlating physical and digital security events. Modern burglar guards with electronic monitoring capabilities can feed alarm events into centralized logging platforms, enabling security teams to correlate attempted physical intrusions with network reconnaissance or social engineering attempts targeting the same facility.
Raw log data arrives in hundreds of formats-syslog, JSON, XML, CEF, LEEF, and proprietary schemas. Enterprise security Splunk uses props.conf and transforms.conf configurations to parse these formats into normalized Common Information Model (CIM) field names.
Proper CIM compliance ensures that correlation searches work consistently across vendors. Authentication events from Windows Active Directory, Linux PAM, cloud identity providers, and VPN concentrators all map to standardized fields like src_user, dest, and authentication_method. This normalization allows a single detection rule to identify password spray attacks regardless of the target system.
Field extraction performance impacts search speed and indexer resource consumption. Heavy forwarders should perform the majority of parsing and enrichment before data reaches indexers, reducing CPU load on the indexing tier. Regular expression optimization and indexed field extraction accelerate searches that filter on high-cardinality fields.
Moving beyond out-of-the-box content requires custom detection development aligned with your organization's threat model and risk profile. Security engineering teams build correlation searches, risk rules, and threat intelligence lookups tailored to their unique environment.
Statistical modeling identifies deviations from established baselines-users accessing unusual files, systems communicating with rare destinations, or processes exhibiting abnormal resource consumption. Enterprise security Splunk supports machine learning toolkit (MLTK) algorithms for clustering, classification, and forecasting.
Common behavioral detection patterns include peer group analysis comparing user activity against departmental norms, time-series forecasting to identify unusual volume spikes, and sequence modeling to detect out-of-order process executions. These techniques complement signature-based detections by catching novel attacks that evade known indicators.
Enterprise security Splunk ingests threat intelligence from commercial feeds, open-source repositories, and internal research. Intelligence appears as automatic lookups enriching events with context-known malicious IPs, compromised domains, file hashes associated with malware families, and SSL certificate fingerprints linked to threat actors.
CISA advisories provide actionable indicators that security teams incorporate into detection logic, while industry-specific information sharing organizations contribute sector-relevant threat data. Intelligence management workflows include indicator expiration, confidence scoring, and false positive feedback loops.
The platform supports STIX/TAXII integration for standardized threat intelligence exchange and RESTful APIs for custom feed ingestion. Threat intelligence correlation adds critical context during investigations, helping analysts determine whether observed activity aligns with known adversary tactics.
Regulatory frameworks increasingly mandate centralized security monitoring and incident documentation. Enterprise security Splunk addresses compliance requirements for standards including PCI DSS, HIPAA, GDPR, SOX, and ISO 27001 through preconfigured reports and audit trails.
NIST guidance on modern log management practices emphasizes tamper-evident storage and chain-of-custody preservation for security logs. Splunk's index immutability ensures that once data is written, it cannot be modified or deleted without leaving forensic evidence.
Compliance teams configure data retention policies matching regulatory requirements-seven years for financial records under SOX, six years for healthcare data under HIPAA. SmartStore architecture allows long-term retention on cost-effective object storage while maintaining search accessibility for investigations and audits.
Report automation delivers scheduled compliance artifacts:
Organizations handling personally identifiable information implement data masking and pseudonymization within enterprise security Splunk. Field-level redaction obscures sensitive elements like Social Security numbers, payment card data, and healthcare identifiers while preserving analytical value.
Role-based access controls restrict visibility to authorized personnel, with separate data indexes for different sensitivity classifications. Audit logging tracks all searches and data access, supporting non-repudiation requirements and insider threat detection.
The shift toward cloud infrastructure requires enterprise security Splunk architectures that span on-premises data centers, public cloud regions, and software-as-a-service applications. Modern deployments leverage Splunk Cloud Platform for fully managed SIEM services or hybrid configurations mixing cloud and self-hosted components.
Organizations running workloads across AWS, Azure, and Google Cloud Platform need unified monitoring that normalizes each provider's native logging format. Enterprise security Splunk add-ons for major cloud platforms ingest CloudTrail, Azure Activity Logs, and GCP Audit Logs into CIM-compliant data models.
Cloud-specific detections identify misconfigurations, overly permissive IAM policies, unencrypted storage buckets, and suspicious API activity. Cloud Security Alliance guidance on monitoring and zero-trust architectures recommends centralizing telemetry from cloud control planes, container orchestrators, and serverless function execution environments.
Container security monitoring captures orchestration events from Kubernetes, Docker, and service mesh platforms. Microservices architectures generate high-volume distributed tracing data that enterprise security Splunk correlates to detect lateral movement between containerized workloads.
Software-as-a-service applications constitute blind spots in traditional network-focused monitoring. Enterprise security Splunk integrates with SaaS platforms through API connectors and webhook receivers, ingesting authentication logs, file sharing activity, email security events, and collaboration platform usage.
Critical SaaS data sources include Microsoft 365 unified audit logs, Salesforce event monitoring, Okta system logs, and cloud access security broker (CASB) telemetry. These feeds enable detection of account takeovers, data exfiltration through sanctioned cloud apps, and shadow IT usage.
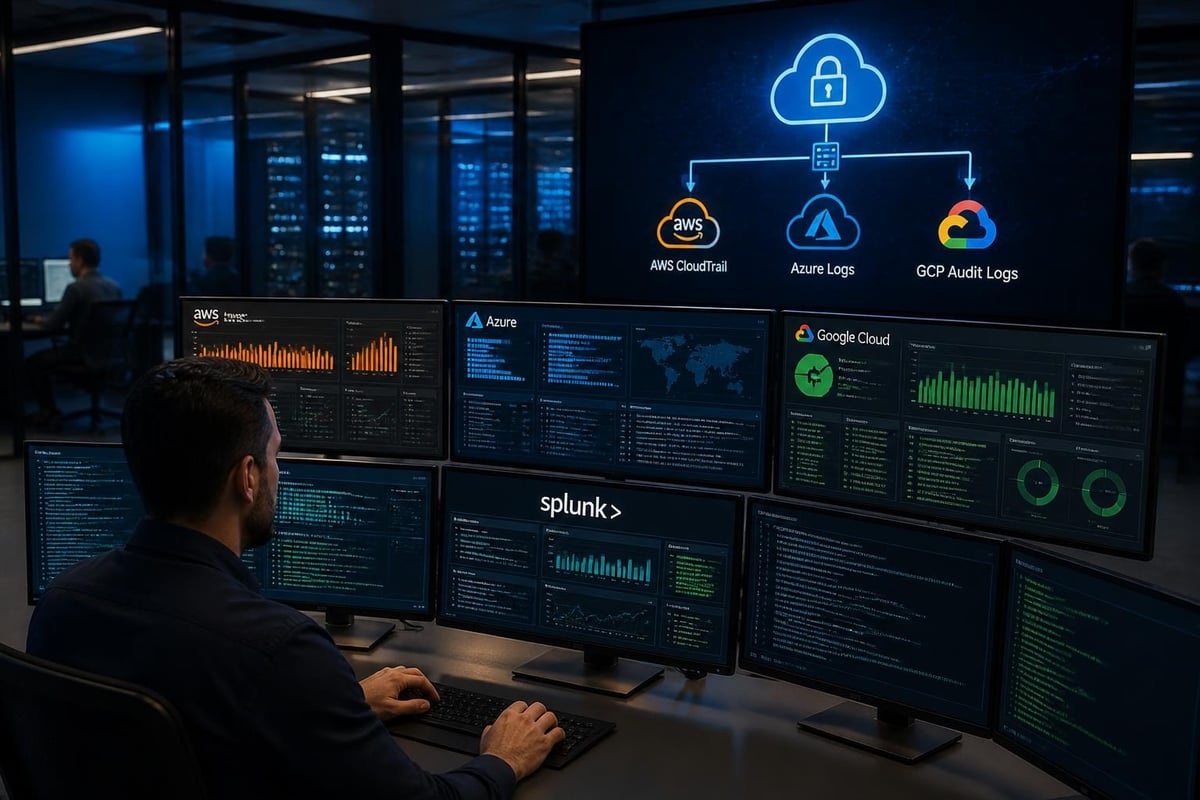
Maximizing return on enterprise security Splunk investment requires operational discipline, continuous improvement, and skilled personnel. Security operations centers evolve through maturity stages from reactive alert triage to proactive threat hunting and adversary emulation.
High-performing SOCs treat detection rules as code, implementing version control, peer review, and automated testing for correlation searches. Content development follows a structured process: threat research identifies gaps, detection engineers prototype rules in test environments, validation confirms efficacy without excessive false positives, and deployment follows change management procedures.
Regular content tuning addresses detection drift as environments evolve. Quarterly reviews assess rule effectiveness, suppress noisy false positives, and retire obsolete detections. Integration with MITRE ATT&CK provides a framework for measuring detection coverage across the attack lifecycle, highlighting blind spots requiring new content development.
| Maturity Level | Detection Characteristics | Operational Focus |
|---|---|---|
| Initial | Vendor default rules, high false positives | Alert triage and basic investigation |
| Developing | Some custom rules, inconsistent tuning | Process documentation, metrics collection |
| Defined | Standardized content lifecycle, regular tuning | Threat hunting, proactive monitoring |
| Managed | Risk-based prioritization, automated response | Adversary simulation, purple team exercises |
| Optimizing | Continuous improvement, ML-enhanced detection | Threat intelligence production, peer collaboration |
Mature organizations complement automated detection with hypothesis-driven threat hunting, where analysts proactively search for signs of undetected compromise. Enterprise security Splunk provides the data foundation and analytical flexibility for hunting campaigns targeting specific adversary techniques.
SANS Institute research on threat hunting methodologies emphasizes iterative investigation workflows that generate new detection content. Hunters formulate hypotheses based on threat intelligence, execute exploratory searches across historical data, validate findings through additional pivots, and document novel indicators or behaviors for automated detection.
Purple team exercises combine red team offensive tactics with blue team defensive capabilities, validating that enterprise security Splunk detects simulated attacks. These controlled scenarios test detection coverage, alert triage procedures, and incident response playbooks under realistic conditions.
As data volumes grow, enterprise security Splunk deployments require ongoing performance optimization to maintain search responsiveness and alert generation timeliness. Common bottlenecks include inefficient correlation searches, under-resourced indexers, and poorly designed data models.
Search optimization techniques include:
Capacity monitoring tracks indexing lag, search concurrency, disk utilization, and CPU consumption across the cluster. Proactive scaling prevents performance degradation as security monitoring scope expands.
Enterprise security Splunk functions as a central nervous system for broader security architectures, integrating with endpoint protection platforms, network security tools, identity governance systems, and vulnerability scanners. These integrations enable both data collection and automated response orchestration.
Security orchestration, automation, and response (SOAR) platforms consume alerts from enterprise security Splunk and execute predefined playbooks-isolating compromised endpoints, disabling user accounts, blocking malicious domains at the firewall, or creating tickets in IT service management systems.
Bidirectional integration allows SOAR platforms to push investigation outcomes back into Splunk, closing the feedback loop for alert disposition and enriching historical data with analyst notes. This integration accelerates incident response while reducing analyst burnout from repetitive manual tasks.
Enterprise security Splunk notable events automatically generate incidents in platforms like ServiceNow, Jira, or PagerDuty. Ticketing integration provides business process workflow around security events-assignment to on-call analysts, escalation procedures for high-severity incidents, and SLA tracking for investigation timelines.
Case management features within ES maintain investigation state, attach evidence artifacts, and document analyst actions. Integration with knowledge management systems captures lessons learned and improves playbook documentation for future incidents.
Enterprise security Splunk delivers comprehensive visibility and analytical depth for modern security operations, enabling organizations to detect sophisticated threats, investigate incidents efficiently, and maintain compliance across hybrid environments. When you're ready to strengthen physical security measures that complement your digital defenses, Limax Security Specialists offers expert installation of burglar guards, security gates, and protective barriers designed for South African homes and businesses-because comprehensive security requires both cyber awareness and physical protection.


